Wedding Website Platforms That Market to Your Guests Without Disclosure
Free wedding sites profit by selling your guests' personal data to vendors without telling anyone.
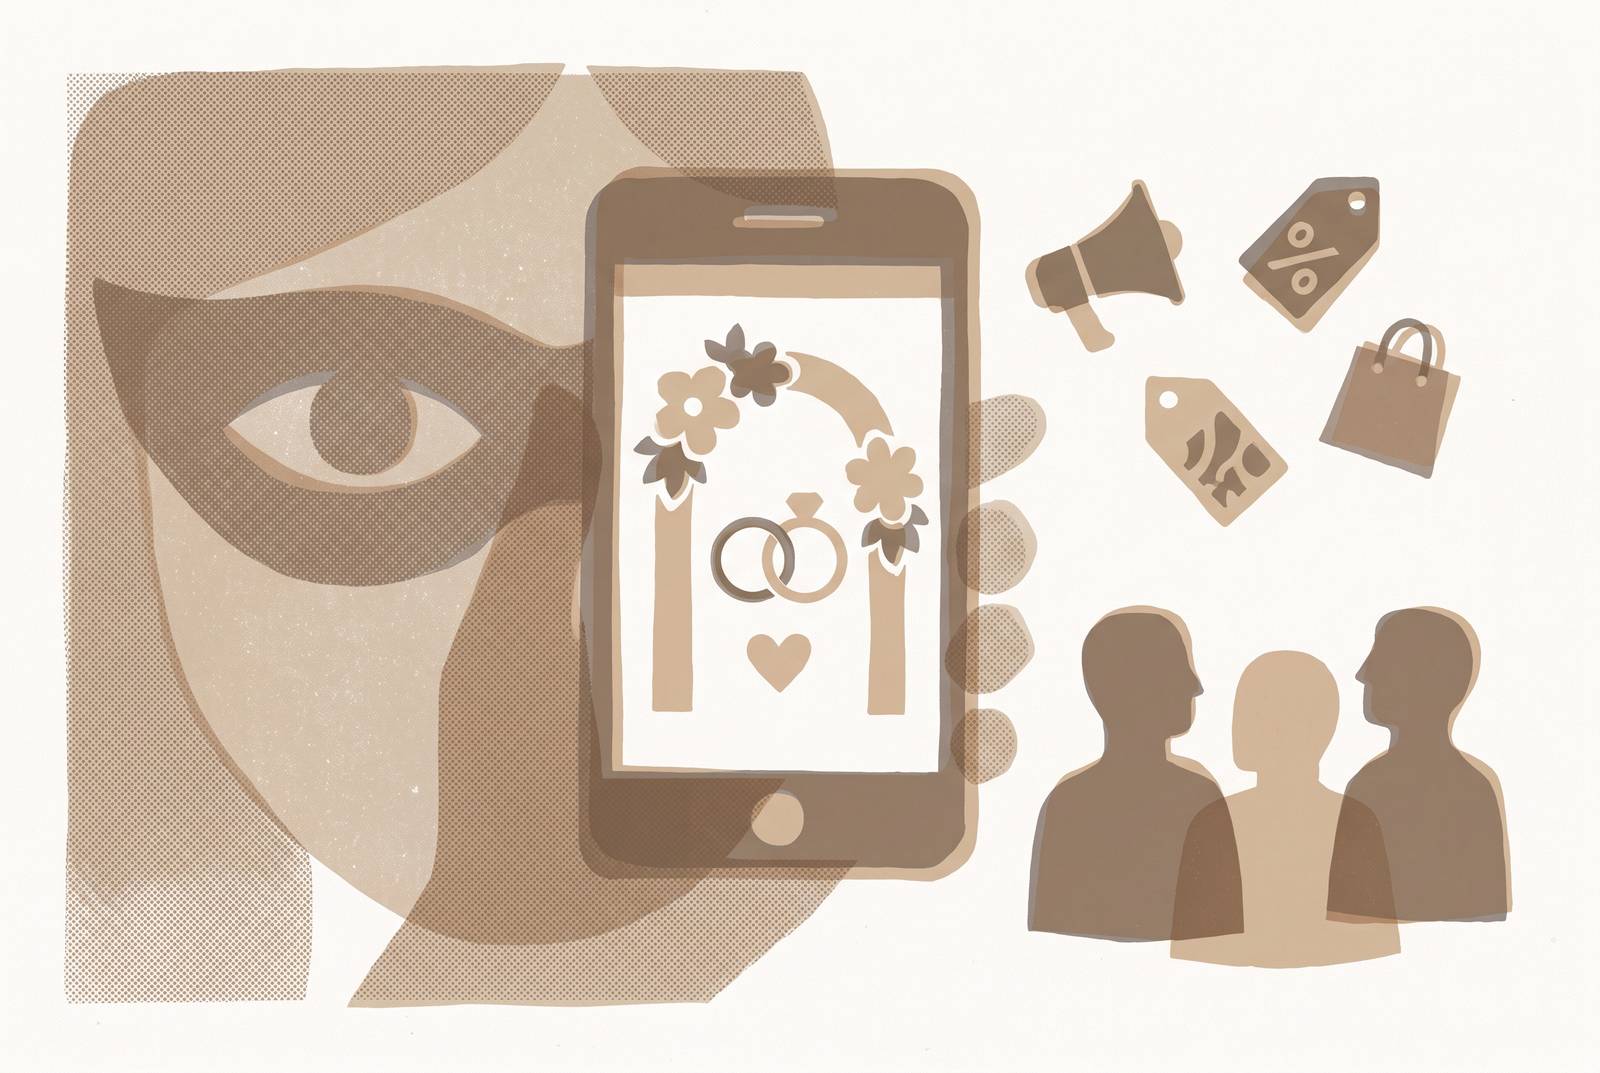
Free wedding websites are not free. The couple pays nothing because vendors do, and the currency that changes hands behind the scenes is the guest list: names, addresses, dietary needs, relationships, spending signals, all of it sitting inside a system built to sell access to an audience of engaged couples and the people around them.
How free wedding platforms make money
A wedding website platform that charges nothing still has to pay its staff, its servers, its marketing budget. That money comes from somewhere, and in this market it almost always comes from vendors: photographers, caterers, florists, venues, all paying for a subscription that puts them in front of couples actively planning a wedding. The couple is not the customer in this arrangement. The vendor is.
This changes what the platform is actually built to do. Every RSVP a guest submits adds a name, an email, a home address, a dietary note, a note on how they relate to the couple, all of it landing inside a database whose value to the business comes from how well it can be sold to paying vendors. A "recommended supplier" badge on a vendor's listing is a placement someone paid for, the same way a sponsored link sits above the organic search results.
The wedding planning market right now splits roughly into two kinds of platform: big all-in-one ecosystems that try to handle every part of planning in one place, and smaller niche tools that do one or two things well. Both kinds can run on this vendor-subscription model. The all-in-one platforms just tend to do it with the fullest possible picture of the wedding, because they are the ones holding the budget, the guest list, the registry, and the vendor enquiries all in one system. None of this gets explained to a couple at signup. The terms of service might gesture at "third-party partners," but the plain sentence, "we make money by selling vendors access to your guest list," does not appear on the homepage.
What data flows through a wedding website
Once a couple builds a wedding website and starts collecting RSVPs, the amount of personal information sitting inside that one platform is bigger than most people would guess.
Start with what the couple themselves hands over just by building the site: the wedding date, the venue and its location, roughly how many guests are coming, hints about the budget through which vendors get contacted, and a running record of vendor preferences and spending patterns as choices get made.
Then there's everything guests contribute. Full names. Home addresses, often needed for save-the-dates or physical invitations synced through the platform. Email addresses and phone numbers. Dietary requirements, which routinely shade into medical information: allergies, intolerances, conditions that affect what someone can eat at a sit-down dinner. How each guest relates to the couple, whether they're attending the ceremony, the reception, or both.
On top of that sits behavioral data: which pages a guest clicked through on the website, whether they browsed the registry and what they looked at, what device they used, roughly where they were when they accessed the site.
Those three layers together form a strikingly complete marketing dataset. It maps an entire social network, the full guest list, and ties that network to a specific date that is already known months in advance. Then it attaches spending intent to named individuals through registry activity and vendor enquiries. Few other everyday tools build a profile this complete, this fast, with this little friction.
The dietary and medical information deserves particular attention, because it sits at the more sensitive end of what personal data usually looks like. A guest filling in an RSVP form with "nut allergy" or "coeliac" is answering a practical catering question. Almost none of them would expect that detail to end up visible inside a vendor marketplace built to sell them services.
The consent gap: guests who RSVP never agreed to any of this
The couple signs up for the platform and, somewhere in that process, agrees to its terms of service. The guest never does any of that.
A guest's experience is far simpler and far less informed. They get a wedding invitation from someone they trust, click through to a website, type in their name, their address, their dietary needs, confirm they're coming, and submit. At no point in that process does anyone tell them they've just entered a database that vendor subscribers can access. There's no checkbox, no disclosure, no moment where the system pauses to say what happens to this information next.
This is where the couple's role matters most, and where the argument gets uncomfortable. The couple didn't build the vendor marketplace, and they didn't write the privacy policy. But they're the ones who sent the invitation. They're the ones their guests trusted when they clicked the link. In effect, the couple becomes the unwitting conduit between people who trust them and a commercial system those people never agreed to join, built on a revenue model the guests have no way of seeing.
This gap raises a short list of serious questions that privacy discussions about these platforms keep coming back to: how guest list data actually gets protected once it's inside the system, whether any of it is sold or passed to third parties beyond the vendor marketplace itself, and how long the platform holds onto that data after the wedding is over and the account goes quiet. Guest exposure doesn't stop at the moment of collection, either. Many of these platforms share meaningful amounts of guest data directly with vendors as part of the marketplace model. That creates multiple separate points where that information can end up somewhere the guest never imagined.
What Australian law protects against this
Couples in Australia who use an offshore wedding platform generally have fewer practical protections than they'd assume, and the law that might close that gap is still being written.
The relevant piece of legislation is the Privacy Amendment (Personal Data Protection) Bill 2026. Its exposure draft was released on 31 August 2026, and the consultation period on that draft closed on 18 September 2026. One of its proposed changes, a new draft provision on data handling, would require consent before an organization can "trade" personal information. It could cover exactly the kind of arrangement at issue here, where a platform supplies guest contact details to paying vendor subscribers.
Whether that provision would actually apply to a wedding website platform is not settled. The exposure draft doesn't clearly resolve whether a platform that collects guest RSVPs and then makes that data available to vendor subscribers counts as "acting solely as a processor," which matters because the consultation paper suggests the platform will generally carry responsibility for consent obligations unless it's acting solely in that narrower processor role. Until that question gets resolved, couples and guests have no clear answer on which side of the line this business model falls.
Separately, the Spam Act 2003 still governs consent for marketing emails and SMS messages sent to Australians, unless a message qualifies as a designated commercial electronic message exempt from that requirement. The new bill doesn't change this: a separate draft provision specifically keeps the Spam Act outside the new bill's scope, leaving it to operate as its own separate layer of protection.
None of this helps much if the platform in question is based overseas. Offshore platforms serving Australian couples may not actually comply with the Spam Act's consent rules, and if a company has no presence in the country, Australian regulators have limited practical ability to enforce against it. Even where Australian consumer law would otherwise offer a couple a remedy, that remedy becomes much harder to pursue once the data in question has already left Australian jurisdiction. Regulation is moving in the right direction, but it isn't there yet, and it won't retroactively protect data that's already been collected, shared, and sold under the current rules.
Vendor marketplaces create a structural incentive to inflate spending
Privacy isn't the only cost of this business model. A platform that earns its revenue from vendor subscriptions has a built-in reason to push couples toward spending more, not less.
The logic runs in a straight line. Vendor listings are paid placements, so the more money couples spend with those vendors, the more valuable the platform's audience becomes, and the more vendors are willing to pay for access to it. A "recommended" tag next to a vendor's name is a purchased position, not an independent judgment about who's worth hiring. And because the platform's income depends on vendor spending rather than on helping couples stick to a budget, it has little reason to flag the costs that would shrink the final bill: corkage fees, cake-cutting charges, mandatory gratuity add-ons, and the other line items that tend to surprise couples after the contract is signed.
There's a fair counter-argument here, and it deserves to be taken seriously. Vendor marketplaces do create real value, which is genuine and explains these platforms' popularity: they aggregate reviews, give couples some way to hold vendors accountable for bad service, and subsidize planning tools that couples would otherwise have to pay for out of pocket.
But if you're an Australian couple, the trade-off looks worse than it does elsewhere. A lot of the biggest wedding platforms are built in the US, with vendor directories that have few or no Australian suppliers listed. That leaves Australian couples carrying the full privacy cost of the marketplace model (their guest data still flows through the same system) without getting the one benefit that's supposed to justify it: useful, locally relevant vendor recommendations. They get the exposure without the discovery.
What privacy-first platforms do differently
A platform that doesn't run a vendor marketplace has no paying vendor customers to hand guest data to. That removes the core financial reason to treat that data as a sellable asset.
That's the clearest test of whether a platform's privacy claims mean anything in practice. If there's no vendor marketplace, there's no commercial buyer for guest information, and the data has nowhere to go except between the couple and the people helping them plan. Compare that to a platform that advertises itself as privacy-conscious while still running vendor subscriptions in the background. A privacy policy is a document. A revenue model is a structure, and the structure is what actually predicts behavior.
These trade-offs deserve to be named honestly. Marketplace-funded platforms cost nothing upfront, and they offer a wide, searchable directory of vendors in one place, which genuinely saves couples time. Platforms that skip the marketplace model may charge something for premium features, such as Minted's one-time $15 annual upgrade for a custom URL (its password protection, notably, comes free on the standard tier). Couples using a privacy-first platform may also have to do more of their own vendor research. The marketplace model saves couples real time by putting a wide, searchable vendor directory in one place. So is the cost it extracts from guests who never signed up for it.
What to check before handing over your guest list
Before entering a single guest's name, address, or dietary note into any wedding website, a couple can run through a short set of questions that will tell them almost everything about how that platform actually treats the data it collects.
Start with the business model itself: does this platform run a vendor marketplace, and if it does, are those vendor listings paid subscriptions or independent recommendations? Then read the privacy policy specifically for what it says about sharing guest data with third parties, and check whether that information gets disclosed to guests at the actual point of RSVP, not just buried somewhere in the couple's own terms of service that guests never see. Ask how long the platform holds onto guest data once the wedding date has passed, and whether that data can be exported or deleted on request if the couple decides they want it gone. Find out whether the platform falls under Australian law or whether its data processing happens offshore, because that single fact decides what recourse you have if something goes wrong. Ask what the platform's revenue model actually is and who its paying customers are, because that answer predicts almost everything else about how guest data gets treated.
But you should understand password protection on its own terms, separate from these questions. Many platforms offer it as a way to keep a wedding website from showing up in public search results, and it's a genuinely useful feature for that purpose. But it has nothing to do with what happens to guest data once it's inside the platform's own systems and accessible to vendor subscribers. Those are two entirely separate problems, and solving one does nothing for the other.
For Australian couples, jurisdiction determines what recourse they actually have. A platform built for the Australian market, priced in Australian dollars, and governed by Australian law gives couples and their guests a clearer path to recourse than an offshore platform whose privacy policy quietly points back to US jurisdiction. The simplest test cuts through all the fine print: if a platform's revenue comes from vendors paying for access to an audience, the guest list is that audience, whether or not the privacy policy says so in plain words.